Where most products are
Selling to customers in the EU or UK means building for GDPR: what you collect, where it lives, who can reach it and how quickly you can export or delete it. We design those answers into the data model from the start, working alongside your compliance lead or advisor.
What we build in for GDPR
Data where it should live
We host your database, auth and files in an EU region, such as Supabase in Frankfurt or Ireland, and make sure backups, logs and other vendors follow the same plan.
Consent and only the data you need
We collect only what the product uses, record consent where it is required and keep each purpose separate, so your privacy notice matches what the product actually does.
Export and deletion on request
Users can download their data or have it deleted across the database, files and connected tools, so access and erasure requests become a routine task for your team.
Privacy designed by role
Managers and admins often need patterns, not individual records. We decide who can see what for every role before designing any screens, then enforce it in the database.
How it works
- 01
Map the data
On free calls we map the personal data you hold, where it lives and who touches it, then agree scope and price before any work starts.
- 02
Build or fix
Regions, consent, access rules, export and deletion, with working software every week. The engineer doing the work is on your calls.
- 03
Hand over and support
We hand over the code, docs and a record of every safeguard you can show a buyer, and stay on for support, or on a retainer as the product grows.
I hired Zeroic for a fixed-scope MVP of Performalise two-and-a-half years ago. They built the data pipeline, the AI sprint health models, the SOC 2 data layer - and they're still on retainer. Says most of what I need to say.
Work we've shipped
AI · HR Tech
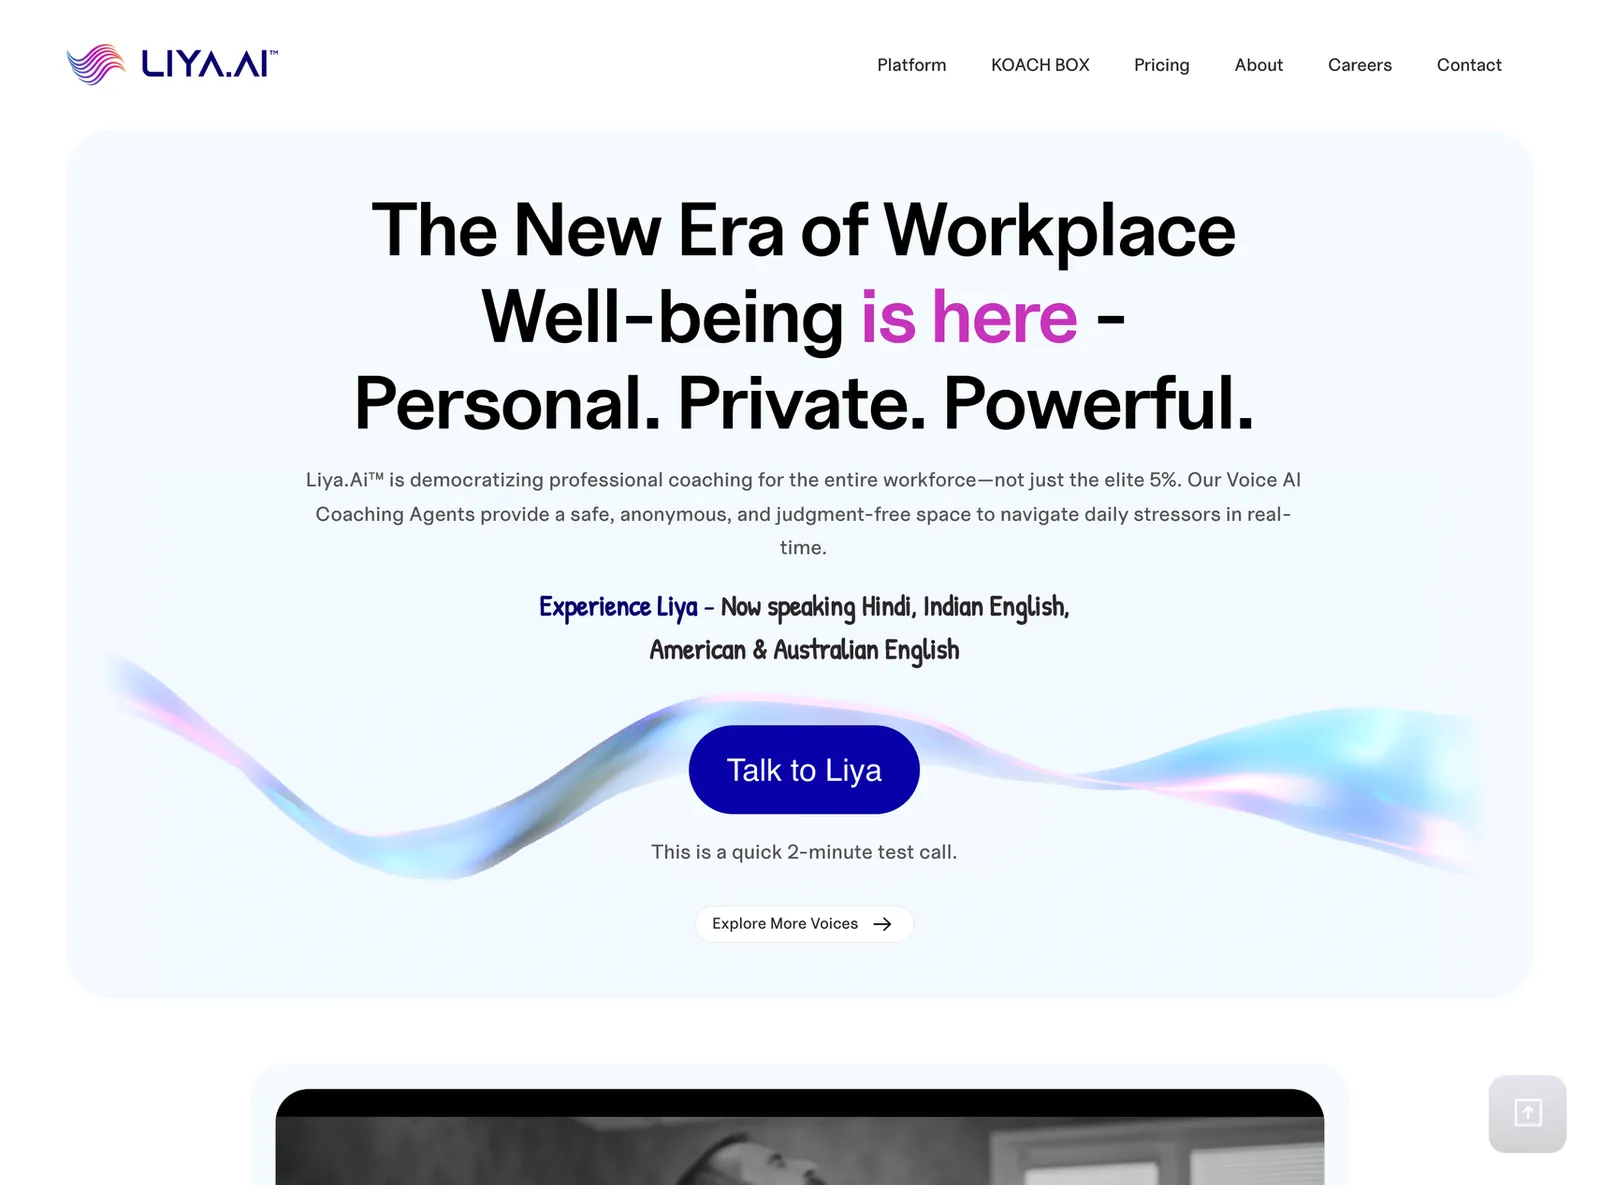
Liya AI
An AI coaching companion for employees, where managers see only aggregated, privacy-first signals.
AI · MVP → Retainer
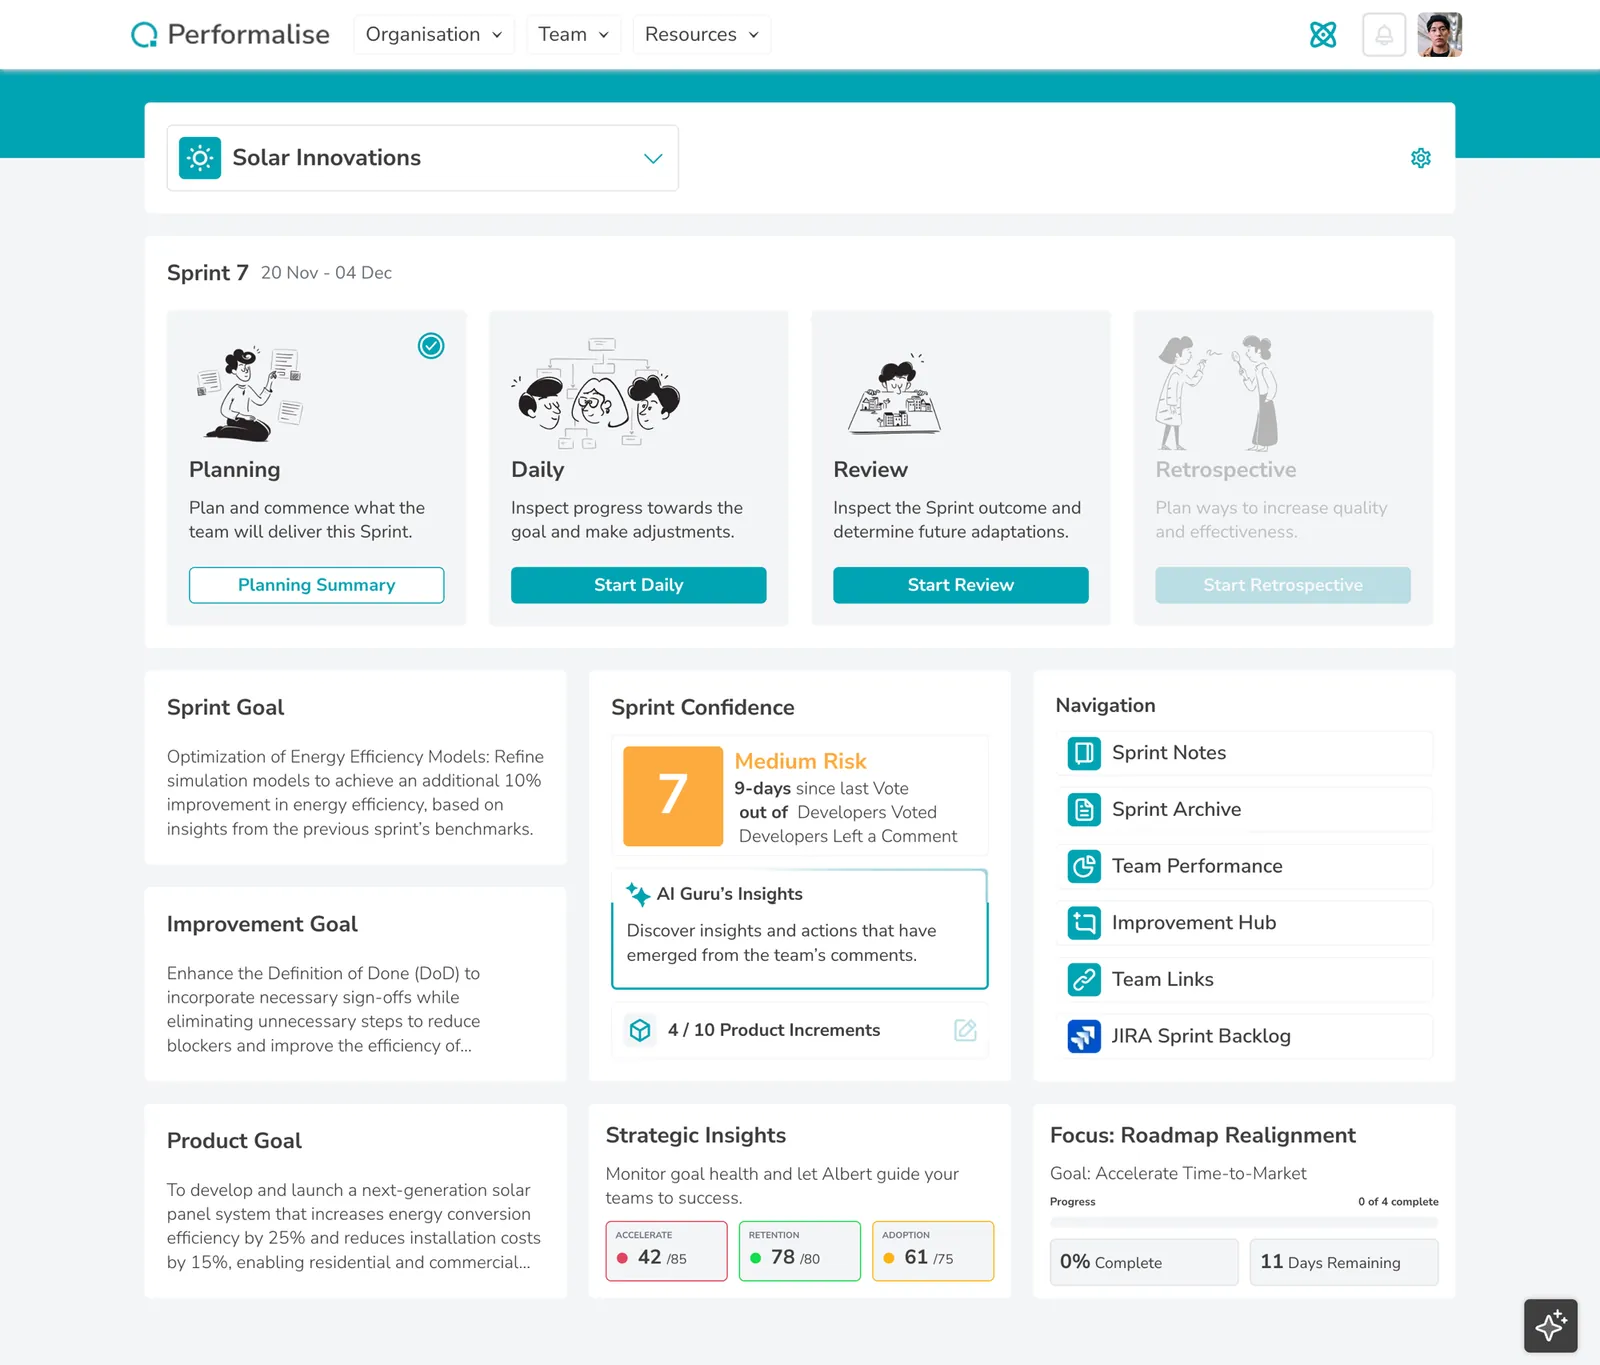
Performalise
An engineering analytics suite for 5+ enterprises. We built its data pipeline, access controls and SOC 2 aligned data layer.
B2B SaaS · Compliance
ComplyAssist
Compliance software with role-based access for in-house teams and consultants. Built in 8 weeks.
How we can help
Four ways to work with us - pick what fits, switch when it doesn’t.
Audits
Find what's broken - or whether AI is worth it - before you build.
Learn moreMVP Sprint
Zero to production in 5-6 weeks. A real product, not a prototype.
Learn moreRetainer
A senior engineer embedded on your team, month to month.
Learn moreCode Rescue
Vibe-coded app breaking under real users? We rebuild it to hold.
Learn moreFAQ
Frequently asked questions
Can you build a GDPR compliant app?
Yes. We build to GDPR requirements: EU hosting where you need it, consent where it is needed, role-based access, export and deletion, and vetted vendors, designed in from the start.
Can our data stay in the EU?
Yes. We deploy your database, auth and storage to an EU region, such as Supabase in Frankfurt, Ireland or Paris, and keep backups, logs and other vendors in line with it.
Does this cover UK GDPR as well?
Yes. UK GDPR, as updated by the Data (Use and Access) Act 2025, keeps the same core principles, so the same safeguards apply, and we host in London where UK data residency matters to you.
Can you make an existing product GDPR-ready?
Yes. We map the personal data you hold, then add what is missing, such as EU hosting, export, deletion and access rules, without changing what your users see.
How much does GDPR work cost?
A new product is an MVP Sprint: one fixed price, agreed before the build. Sprints start at $12,000. Already live? A Security Audit, from $1,000, maps your personal data, and a retainer builds the changes.
Do we own the code?
Yes, 100%. You own the code, infrastructure, docs and credentials.