Where most Lovable apps are
Lovable gets a real React and Supabase app live fast, and the code is yours. What it leaves unfinished is mostly security and scale: row level security, keys, auth limits and queries that slow down as data grows. We fix those and keep the screens your users know.
What we fix in Lovable apps
Row level security that holds
Most Lovable data leaks come from tables with missing or loose RLS, read through the public anon key in the browser. We write policies per table and test them as real users.
Privileged calls on the server
Secrets in client code and Edge Functions that skip auth checks leak quietly. We move every privileged call behind a server function that checks who is asking first.
Further than the built-in scan
Lovable's security scan flags the critical issues. We go further: storage buckets, webhook signatures, rate limits and every path a row could take out of the server.
Keep building in Lovable after
Lovable syncs to GitHub, so we fix the real codebase and you can keep prompting new screens afterwards, with tests that stop a later prompt from reopening a hole.
How it works
- 01
Review (3 days)
We read the code, the database and the deploy setup, and tell you plainly what to keep, what to fix first and what the fix costs.
- 02
Fix what is failing
Senior engineers lock down RLS, auth and keys first, then the slow queries and integrations, keeping the screens users know.
- 03
Harden and hand off
Tests, monitoring and docs go in before handover. You own the code and every account, with 6 weeks of support under real load.
Starting at $6,000
Fixed scope and fixed price, agreed after the 3-day review. Not sure what is wrong yet? Start with a Security Audit (from $1,000). Need more hands once it is fixed? See senior developer retainers.
Talk to us about your Lovable app  rebuilt our onboarding, shipped our Zapier integrations, and wrote integrated plugins for our proprietary tools - all in record time. He ships better than we spec. This team is literally an extension of mine.
Work we've shipped
Audits · Security + Performance
Audits
Security and performance audits of 100+ live apps, Bubble and Supabase included, with ranked fixes.
AI · MVP → Retainer
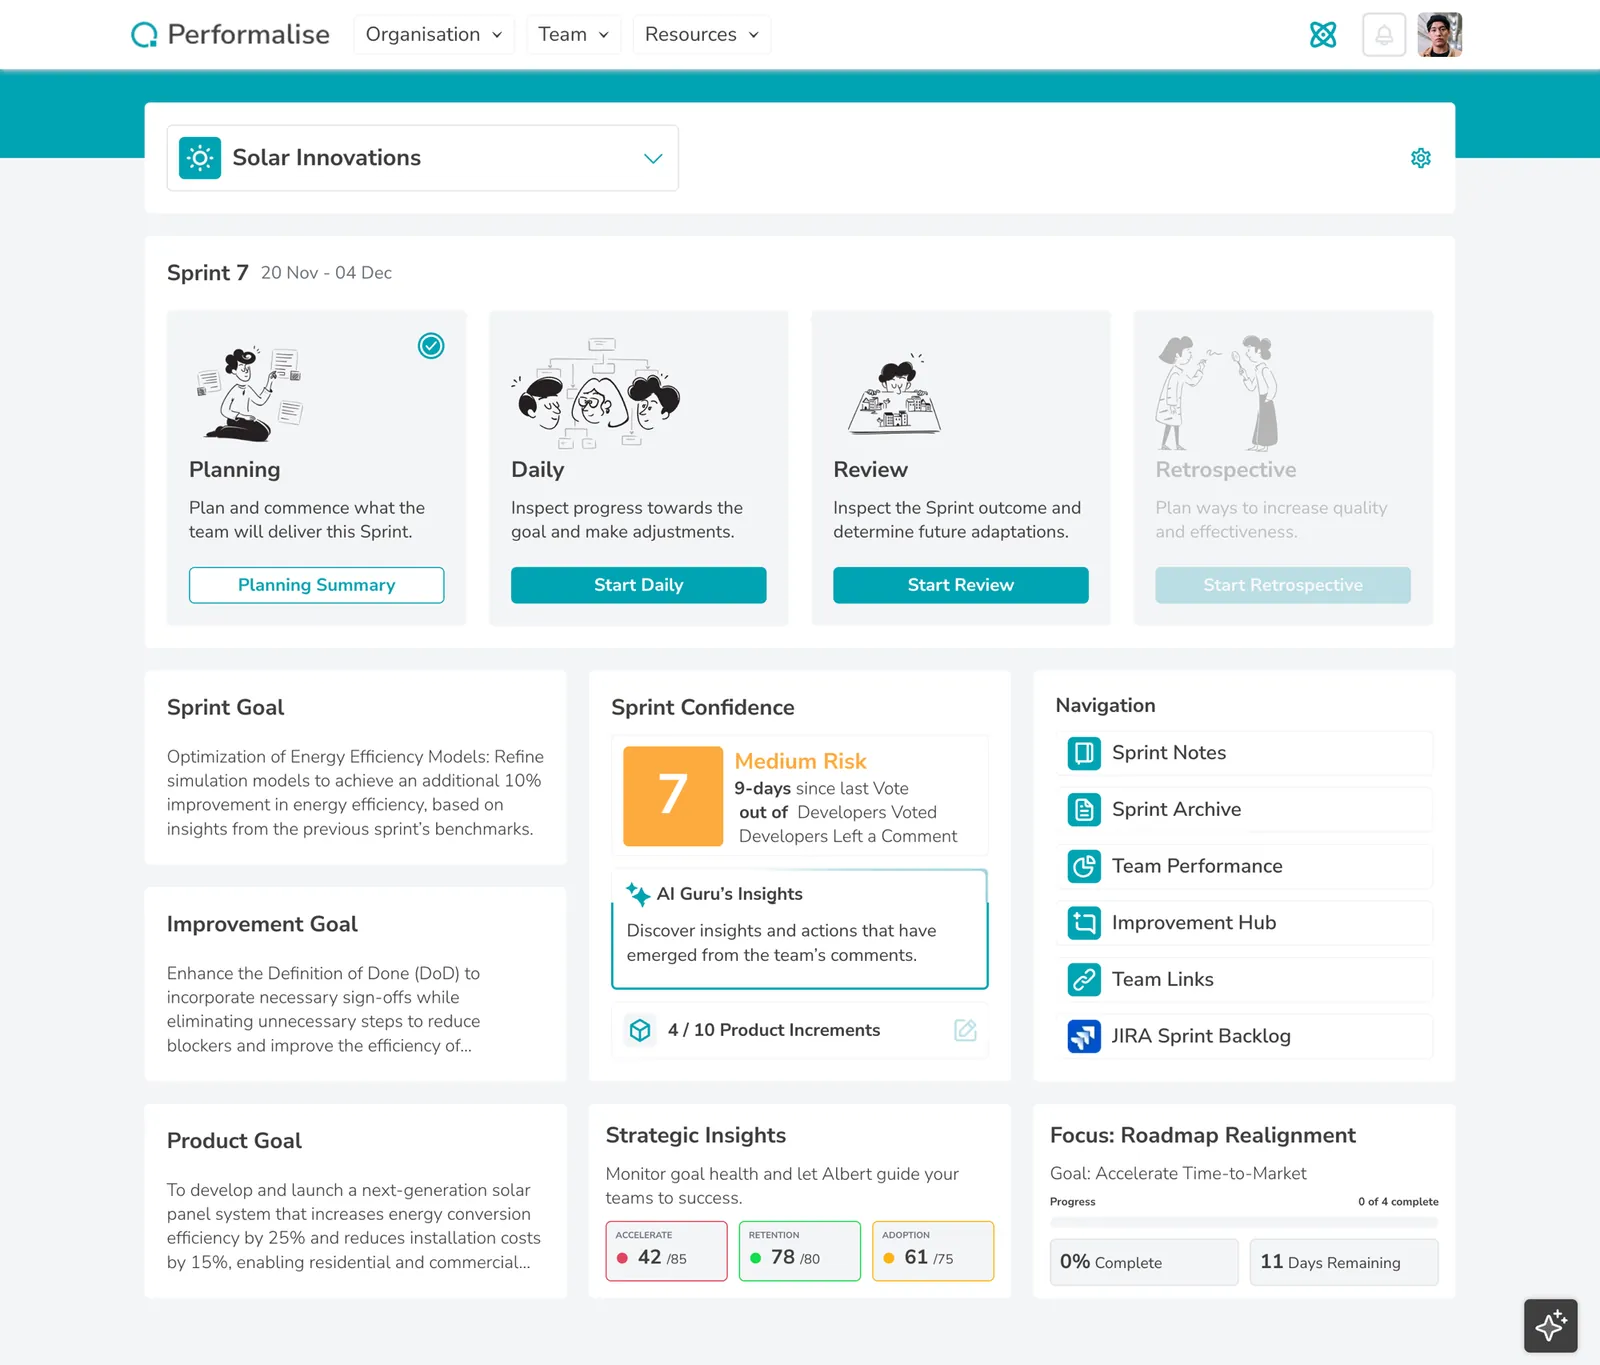
Performalise
An engineering analytics product. We took it from a narrow MVP to a platform 5+ enterprises run on.
AI · Analytics
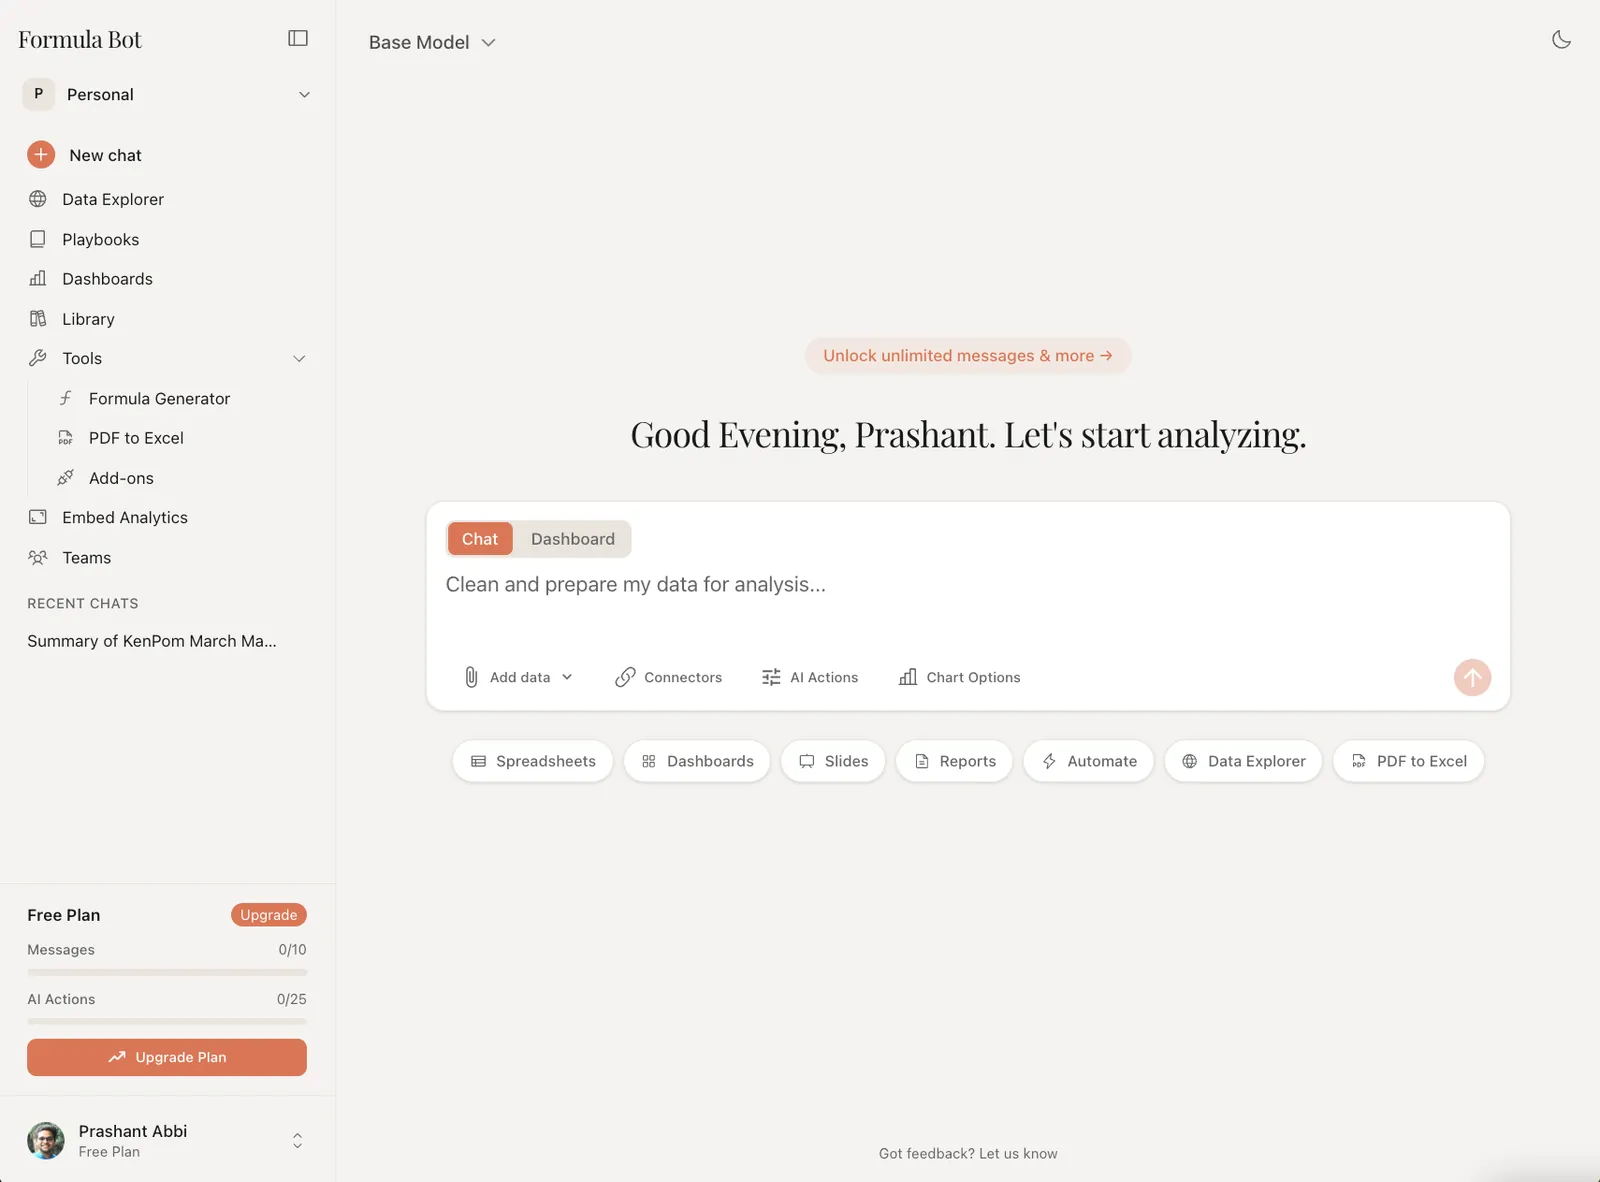
Better Analyst (formerly FormulaBot)
An analytics app used by 1.5M+ people. We built its AI layer as it grew past a million users.
How we can help
Four ways to work with us - pick what fits, switch when it doesn’t.
Audits
Find what's broken - or whether AI is worth it - before you build.
Learn moreMVP Sprint
Zero to production in 5-6 weeks. A real product, not a prototype.
Learn moreRetainer
A senior engineer embedded on your team, month to month.
Learn moreCode Rescue
Vibe-coded app breaking under real users? We rebuild it to hold.
Learn moreFAQ
Frequently asked questions
How much does it cost to fix a Lovable app?
Code Rescue starts at $6,000 for a fixed scope, agreed after a 3-day review. Lovable rescues sit at the lower end of that range, because the code is generally sound and the gaps are mostly security. Not sure yet? A Security Audit, from $1,000, shows what needs fixing first.
Is my Lovable app secure?
Most are close, with a few gaps to close. A 2025 scan of 1,645 Lovable apps found exposed data in 170 of them, mostly through missing row level security. A Security Audit shows where yours stands in 1-2 weeks.
Can I keep using Lovable after the rescue?
Yes. We work in the GitHub repository Lovable syncs to, so you can keep prompting. Tests on the critical paths stop new changes from quietly breaking auth or data access.
Do you rebuild the whole app?
Rarely. We keep what works and rebuild what is failing, usually auth, data access and the integrations everything depends on. Your users keep the same screens.
Do we own the code afterwards?
Yes, 100%. You own the code, database, docs and credentials. No lock-in and no proprietary platform.